iCompaas Inc changelog

New features and improvements shipped in iCompaas.

New

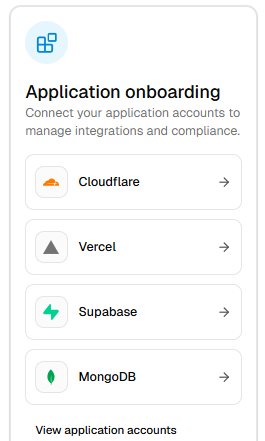
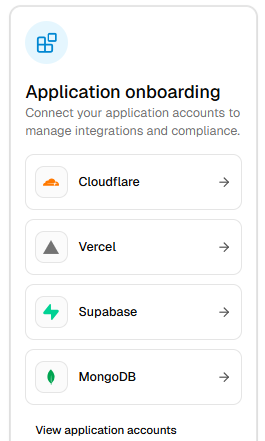
Connect your Cloudflare account directly to iCompaas to continuously assess DNS, TLS, email security, and WAF configuration across your zones.
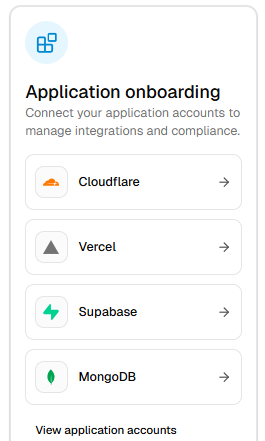
image.png

What you can see:

  • Cloudflare Integration Card with a simple read-only API token setup.

  • Compact Setup Guide with step-by-step instructions shown right below the connection form.

  • Zone-Level Findings showing which domains pass or need attention.

Key benefits:

  • DNS Security detecting subdomain-takeover risks, wildcard records, exposed internal IPs, and missing DNSSEC.

  • Strong Encryption verifying Full (Strict) SSL, TLS 1.2+ with TLS 1.3, Always Use HTTPS, and HSTS.

  • Email & Edge Protection checking SPF, DKIM, DMARC, CAA, WAF with OWASP rulesets, rate limiting, and Bot Fight Mode.

  • 28 Automated Checks mapped to SOC 2, ISO 27001, HIPAA, GDPR, and more.

Cloudflare integration brings your edge and DNS configuration into iCompaas, giving teams continuous, audit-ready evidence for internet-facing security.
iCompaas, Customer Business Team

New

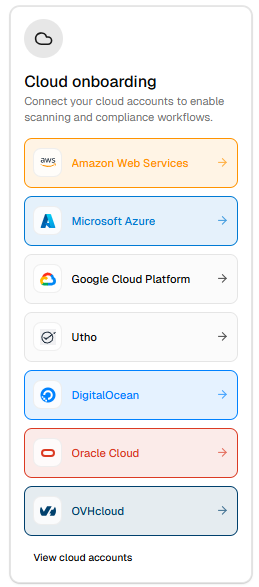
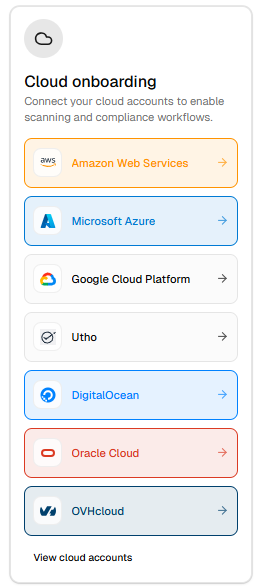
Connect your OVHcloud account directly to iCompaas to automate security compliance scanning and evidence collection across your Public Cloud projects.

image.png

What you can see:

  • OVHcloud Provider Card in the Cloud Onboarding dashboard with secure service-account onboarding.

  • Step-by-Step Setup Guide with the exact IAM policy iCompaas needs, including Logs Data Platform permissions.

  • OVHcloud in Reports so findings appear in your compliance reports with your other clouds.

  • Scheduled Scans that keep your OVHcloud posture continuously up to date.

Key benefits:

  • Account Security Checks covering 2FA, API credential expiry and scope, IAM users, and SSO federation.

  • Centralized Logging Assurance verifying audit, activity, database, and Kubernetes logs are forwarded to Logs Data Platform.

  • Infrastructure Hardening checking private networking, encrypted Object Storage, backups, HTTPS load balancers, and supported versions.

  • 51 Automated Checks mapped to SOC 2, ISO 27001, HIPAA, GDPR, and more.

OVHcloud integration extends iCompaas multi-cloud visibility to European cloud infrastructure, helping teams continuously monitor security posture and stay audit-ready.

iCompaas, Customer Business Team

New

Connect your Oracle Cloud Infrastructure tenancy directly to iCompaas to automate asset discovery, security compliance scanning, and evidence collection.

image.png

What you can see:

  • OCI Provider Card in the Cloud Onboarding dashboard alongside AWS, Azure, GCP, and your other cloud providers.

  • Automatic Scans on Connection with recurring scans scheduled afterwards.

  • Resource-Level Findings showing exactly which OCI resources pass or need attention.

  • Dedicated Cloud Accounts View to monitor OCI alongside your other cloud environments.

Key benefits:

  • Identity & Access Securitychecking MFA, 90-day key and token rotation, password policies, and least-privilege IAM policies.

  • Network & Data Protection detecting open SSH/RDP access, missing flow logs, public buckets, and unencrypted volumes.

  • Continuous Monitoring Readiness verifying Cloud Guard, audit log retention, and event-rule notifications.

  • 52 Automated Checks mapped to SOC 2, ISO 27001, HIPAA, GDPR, and more.

OCI integration brings your Oracle Cloud tenancy into iCompaas, providing centralized visibility into security posture, compliance findings, and evidence across your multi-cloud environment.

iCompaas, Customer Business Team

New

Connect your Supabase organization directly to iCompaas to automate security assessments across authentication, databases, and storage in every project.

image.png

What you can see:

  • Supabase Application Card on the new Application Onboarding page with secure OAuth connection.

  • Organization-Wide Coverage that discovers and assesses every project in your connected Supabase organization.

  • Supabase Provider Icons in your compliance dashboards next to your other cloud and application providers.

  • Connection Diagnostics that clearly explain any setup or permission issues during onboarding.

Key benefits:

  • Authentication Security Checks covering MFA, CAPTCHA, leaked-password protection, and password policies.

  • Database Protection verifying Row Level Security, SSL-only connections, network restrictions, backups, and Point-in-Time Recovery.

  • API & Storage Hygiene checking API key rotation, Edge Function JWT verification, and private storage buckets.

  • 31 Automated Checks mapped to SOC 2, ISO 27001, HIPAA, GDPR, and more.

Supabase integration closes the gap between your application backend and compliance, keeping every project continuously assessed and audit-ready.

iCompaas, Customer Business Team

New

Connect your Vercel team directly to iCompaas to automate security checks and compliance evidence collection across your projects, domains, and team settings.

image.png

What you can see:

  • Vercel Integration Card on the Integrations page with a one-click OAuth install from Vercel.

  • Flexible Project Scope allowing you to connect your whole Vercel team or only selected projects.

  • Vercel Provider Icon across the Frameworks and Controls dashboards alongside your other cloud environments.

  • Automatic Re-scans whenever your Vercel connection changes, keeping findings up to date.

Key benefits:

  • Deployment Protection Monitoring for preview and production deployments, password protection, and Git fork protection.

  • Domain & Certificate Assurance verifying domains, DNS records, and valid SSL certificates.

  • Team Access Governance checking SAML SSO enforcement, SCIM directory sync, owner roles, and stale invitations.

  • 16 Automated Checks mapped to SOC 2, ISO 27001, HIPAA, GDPR, and more.

Vercel integration brings your frontend deployments into iCompaas, giving teams continuous visibility into deployment security and audit-ready evidence.

iCompaas, Customer Business Team

New

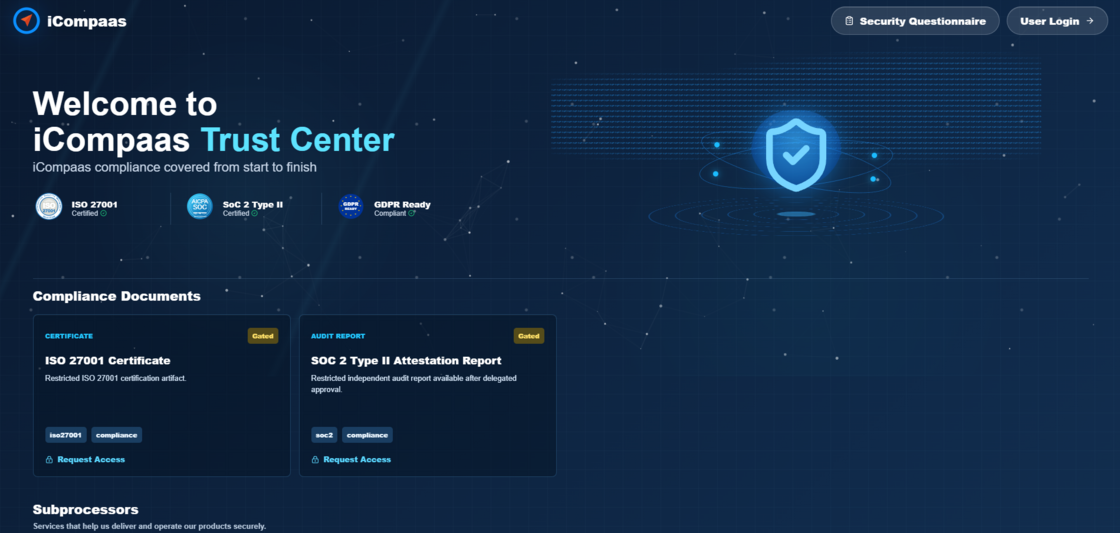
Launch a secure, centralized Trust Center on your custom domain to share your security and compliance posture, manage compliance documents, and control access for prospective buyers and delegated administrators.

image.png

What you can see:

  • Custom Domain & Portal Branding — Host your Trust Center on a custom domain with branded logos, favicons, headers, and authentication configuration.
  • Granular Document Visibility Controls— Set documents as Public for immediate access or Restricted/Gated to require an access request and administrator approval. Documents can also be enabled or disabled from the portal.
  • Delegated Admin Workspace — Allow assigned GRC-OPS delegates to review pending access requests, approve or reject submissions, and revoke previously granted document access.
  • Comprehensive Audit Trail & View History — Track access request lifecycles from Pending → Approved / Rejected / Revoked, with date and time records for each action.

Key Benefits:

  • Accelerate sales & procurement cycles by enabling enterprise buyers to self-serve public compliance documentation without manual email exchanges.
  • Secure Access with Authlee SSO — Authenticate prospective buyers and requesters through Authlee, verify business-domain identities, and provide secure, controlled access to gated compliance documents.
  • Protect sensitive compliance documents by keeping high-value reports behind formal access requests and administrator approval.
  • Reduce compliance workload through Delegated Admin capabilities, automated email notifications for invitations and approvals, and streamlined access revocation.
  • Maintain audit-ready access records with a centralized history of document requests, approvals, rejections, revocations, and access activity.
iCompaas, Customer Business Team

New

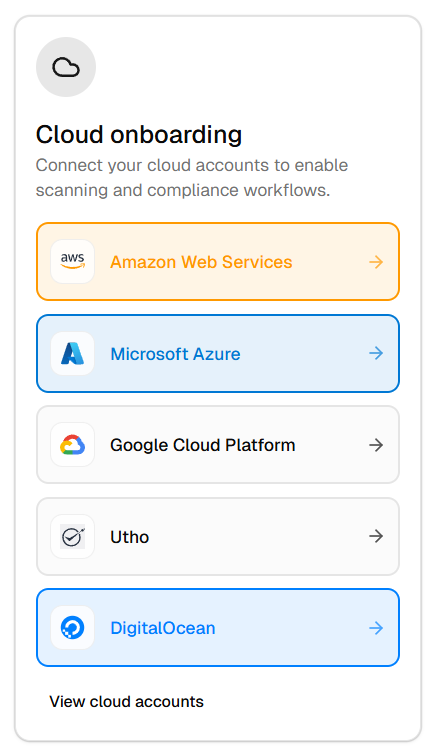
Connect your DigitalOcean account directly to iCompaas to automate asset discovery, security compliance scanning, and evidence collection across your DigitalOcean teams and projects.

Screenshot 2026-08-20 152435.png

What you can see:

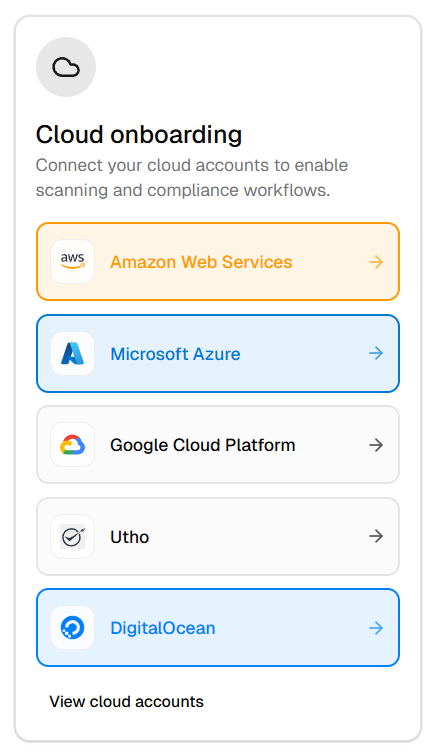
  • DigitalOcean Provider Card in the Cloud Onboarding dashboard alongside AWS, Azure, GCP, and Utho.
  • Automated Personal Access Token Validation to verify authentication and required team permissions during onboarding.
  • Team & Project Inventory providing visibility into available projects within your connected DigitalOcean team.
  • Dedicated Cloud Accounts Filter to monitor DigitalOcean infrastructure alongside your other cloud environments.

Key benefits:

  • Automated Cloud Security Monitoring for supported DigitalOcean resources, including Droplets, Spaces, and Managed Databases.
  • Scoped Read-Only Access using DigitalOcean Personal Access Tokens with the required account:read and project:read permissions.
  • Unified Multi-Cloud Governance bringing DigitalOcean infrastructure into the same compliance and security workflows as your other cloud environments.
  • Centralized Compliance Evidence helping teams maintain consistent visibility and audit-ready evidence across their multi-cloud infrastructure.

DigitalOcean integration brings your cloud projects into iCompaas, providing centralized visibility into security posture, compliance findings, and evidence across your multi-cloud environment.

iCompaas, Customer Business Team

New

Expand your multi-cloud security coverage with native Utho Cloud support for infrastructure scanning, asset discovery, and automated compliance monitoring.

image.png

What you can see:

  • Utho Cloud Onboarding Card alongside AWS, Azure, and GCP in the cloud configuration portal for streamlined integration setup.
  • Asset Discovery & Inventory providing visibility into compute instances, storage volumes, and network resources hosted on Utho.
  • Automated Misconfiguration Detection evaluating Utho cloud resources against configured security and compliance benchmarks.
  • Cloud Risk Breakdown highlighting identified issues by severity with actionable remediation guidance.

Key benefits:

  • Centralized visibility across cloud environments without requiring custom scripts for Utho Cloud.
  • Unified multi-cloud compliance dashboard bringing AWS, Azure, GCP, and Utho Cloud security findings into a single view.
  • Continuous security posture monitoring helping identify cloud misconfigurations and security risks as your infrastructure changes.
  • Simplified compliance management by bringing Utho Cloud infrastructure into your existing security and compliance workflows.

Utho Cloud support extends iCompaas multi-cloud visibility to regional infrastructure, helping teams continuously monitor security posture and maintain audit-ready compliance evidence.

iCompaas, Customer Business Team

New

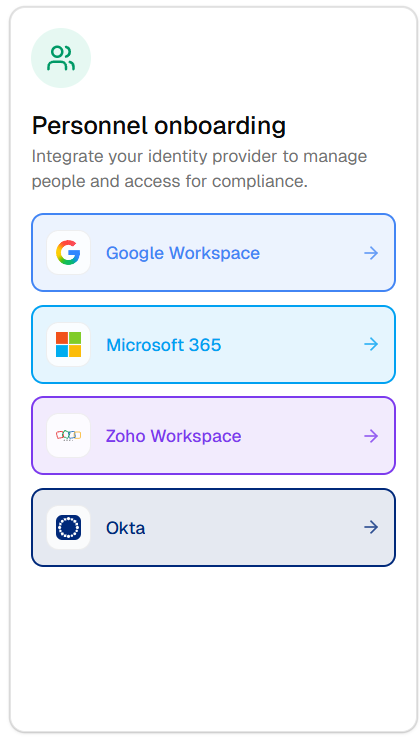
Connect your Okta identity directory directly to iCompaas to automate personnel onboarding tracking, access reviews, and compliance evidence collection.

image.png

What you can see:

  • Okta Integration Card in the Personnel Onboarding Center for seamless, one-click API setup.
  • Unified Personnel Roster that pulls active users, groups, assigned roles, and identity security metrics from Okta.
  • Identity & Access Compliance Status showing MFA enforcement, account status, and access permissions for onboarded personnel.
  • Secure API Credential Storage to protect Okta integration credentials and support compliant API communication.

Key benefits:

  • Eliminate manual employee access audits by syncing personnel data directly from Okta.
  • Verify MFA compliance across onboarded team members to support SOC 2 and ISO 27001 compliance requirements.
  • Maintain continuously updated personnel and access data as team members join, leave, or change roles.

Okta Integration closes the gap between Identity Management and Compliance, ensuring every user account and credential is continuously audited and compliance-ready.

iCompaas, Customer Business Team

New

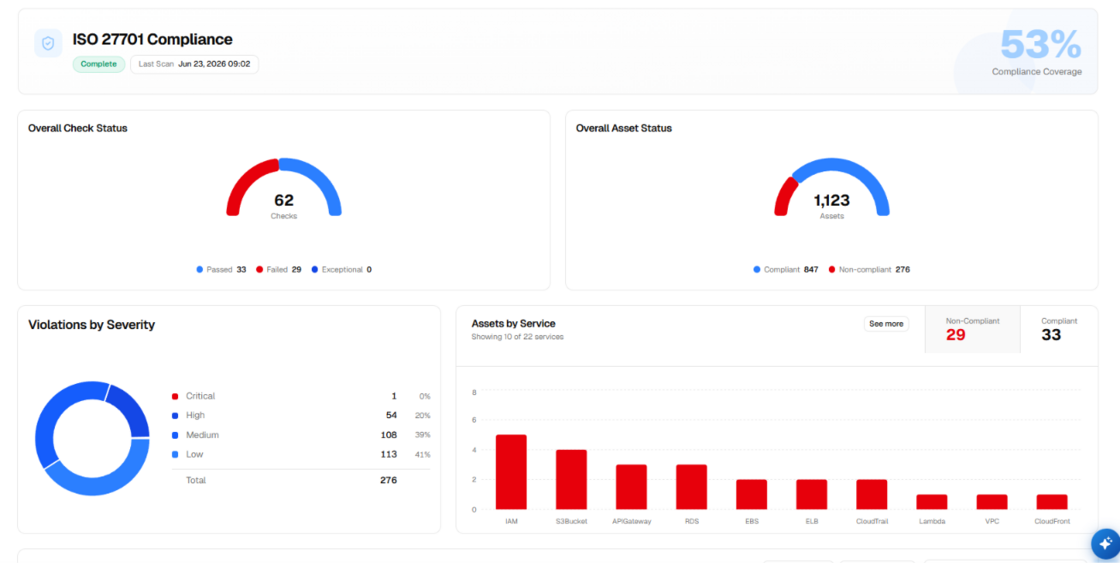
ISO/IEC 27701 is an international standard that introduces a framework for building a Privacy Information Management System (PIMS). It provides clear guidelines and controls to manage Personally Identifiable Information (PII), reduce privacy risks, and demonstrate alignment with global regulations such as GDPR—enabling organizations to build trust, improve compliance readiness, and enhance overall data privacy maturity.

image.png

What you can see:

  • ISO/IEC 27701 standard now available directly in the platform.
  • Automated mapping of existing cloud checks to privacy controls.
  • Compliance reports highlighting data processing status and configuration gaps.
  • Privacy checklists covering consent, retention, and data handling requirements.
  • Step-by-step remediation guidance to resolve privacy control violations.

Key benefits:

  • Generate audit-ready compliance reports instantly.
  • Eliminate duplicate effort through automated control mapping.
  • Strengthen enterprise credibility with recognized privacy standards.
  • Accelerate readiness for third-party and regulatory audits.
  • Support vendor security assessments with clear compliance evidence
  • Simplify management of cross-border data protection requirements.

ISO/IEC 27701 compliance capabilities help organizations streamline data privacy management, ensuring continuous trust with customers and auditors alike.

iCompaas, Customer Business Team